Electronic monitoring has moved a long way from the ankle bracelet that reported a set of coordinates. Early supervision tools were built around one question: where is the device? They assumed the answer to a second question: who is carrying it? That assumption no longer holds. Correctional and community supervision programs now manage far larger caseloads with far fewer officers, creating an urgent need for proof of identity that a standard location ping was never designed to give.
The scale of this shift is worth stating plainly. The Vera Institute of Justice, in its January 2024 census, estimated that roughly 254,700 people were under electronic monitoring in the U.S. criminal legal system, with the total number of monitored individuals growing close to fivefold between 2005 and 2021. Immigration and Customs Enforcement alone pushed its monitored population past 340,000 in late 2022, relying heavily on the SmartLINK smartphone application rather than traditional hardware. Vera also revealed that about 11 companies control roughly 99 percent of the market and that agencies spent more than 1.2 billion dollars on monitoring in 2023. As that population migrated from radio-frequency bracelets to mobile applications, confirming that the correct person is actually holding the smartphone became the central operational challenge.
Liveness detection is the trust boundary that answers this challenge. By verifying that a live, physically present human is on camera during a biometric check, a supervision platform closes the gap between tracking a mobile device and verifying an actual person. The catch, which most vendor marketing glosses over, is that liveness detection is only one of two vital defenses a modern program needs. Confusing the two leaves a program exposed to the exact spoofing attacks it assumes it has solved.
Why Electronic Monitoring Needs Reliable Identity Verification
Legacy platforms leaned on ankle bracelets and fixed landline check-in units. Radio-frequency tethering and basic GPS ankle monitors tracked spatial location well enough, but they carried almost no biometric context. An officer could confirm that a signal sat inside an authorized curfew zone and still have no idea who was standing next to the receiver.
Smartphone applications enabled flexible scheduling and reduced the need for mandatory office visits, but they introduced a new set of weaknesses. A scheduled check-in that asks someone to snap a quick photo or input a PIN proves very little on its own. A PIN can be shared over text. A photo can easily be a snapshot of another photo. Without real-time proof of physical presence, these platforms stay open to identity substitution, where a friend, partner, or paid proxy answers the verification prompt.
Location coordinates compound the problem because they only ever prove that a mobile device sits inside a geofenced area. GPS data cannot tell an officer whether the monitored individual is holding that phone or whether it was left on a kitchen counter while its owner went elsewhere. A curfew system that trusts coordinates alone is really trusting hardware, and hardware does not have a face. Building a compliance record on confirmed human presence, rather than on a phone’s last known position, is what makes that record defensible when a judge asks how an agency verified who checked in.
Where Liveness Detection Fits Into the Monitoring Process
The best place to evaluate liveness detection is inside a single check-in event, which on a well-tuned platform finishes in just a few seconds. Speed is not a luxury here. A check that drags will get abandoned on a weak cellular signal or an aging phone, and an abandoned check reads as non-compliance even when the participant did nothing wrong.
A standard remote check-in runs through a short, ordered sequence where each stage exists to neutralize a specific bypass attempt:
- Trigger: The platform fires an automated check-in request via push notification, operating on a scheduled or randomized window. Randomization matters because predictable check-in schedules are the easiest to arrange a proxy for.
- Camera Activation: The participant opens the secured application, which controls the camera hardware directly rather than allowing an uploaded image from the device gallery.
- Face Capture: The interface frames the face and adjusts for available ambient light, guiding the subject into a usable position instead of triggering a failure over a slightly tilted phone.
- Liveness Check: Algorithms read micro-movement, depth signals, skin texture, and light reflection to decide whether a living face is present.
- Identity Match: The captured facial sample is compared one-to-one against the enrolled template for that specific individual, rather than searched against an open database.
- Logging Event: On success, the system records the timestamp, the exact GPS coordinates, and the confirmed identity as a single cryptographic entry.
- Exception Routing: If liveness fails or the biometric match score falls below set thresholds, the case escalates directly to a supervising officer instead of silently passing or failing.
Chaining these operational steps is what stops the two simplest evasions: stalling until the check-in window passes and holding up a static image to satisfy the screen prompt.
Common Fraud Attempts That Liveness Detection Is Designed to Stop
People under strict curfews or court-ordered movement restrictions have real incentives to defeat identity checks. These attack methods sort into a clear ladder of technical effort and cost.
The cheapest spoofing method is the printed photograph, where someone holds a high-resolution print of the enrolled person in front of the lens. Liveness engines catch this attempt routinely by looking for natural depth, subsurface skin properties, and dynamic micro-movements that a flat sheet of paper cannot reproduce.
A step up in sophistication is the screen replay attack, where a pre-recorded video of the participant plays back on a second phone or tablet. Advanced detectors flag the pixel grid of the target display, moiré interference patterns that form when one screen films another, and artificial frame rates that do not match a live environment.
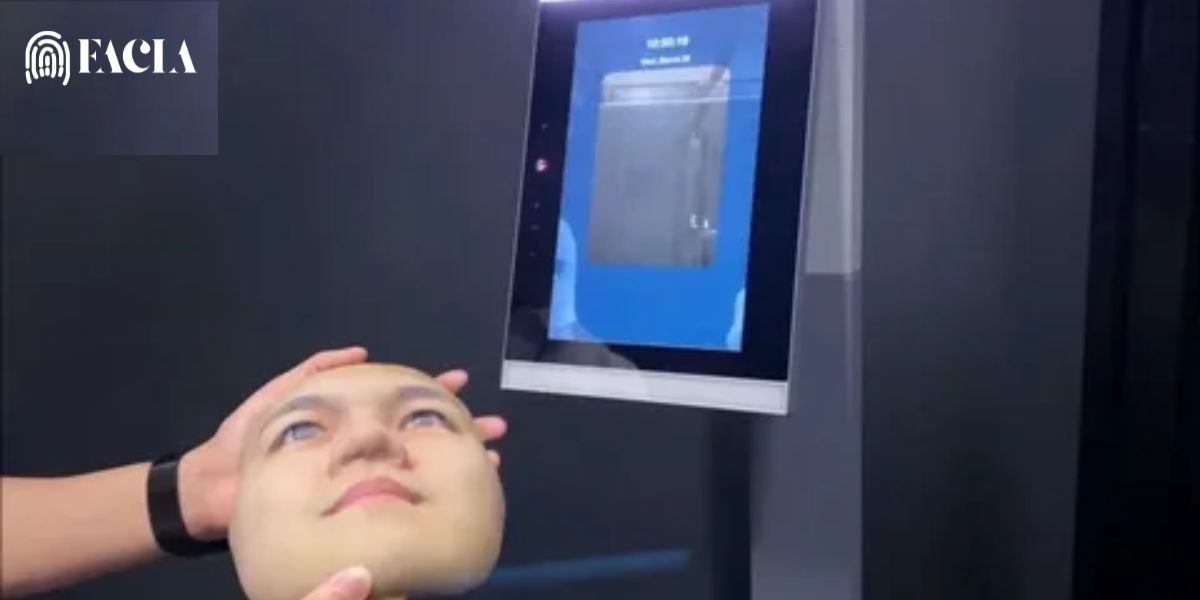
Silicone masks and 3D-printed facial models raise the physical threshold considerably. These try to reproduce three-dimensional human dimensions, making physiological defenses essential. Remote photoplethysmography, often called rPPG, reads the faint color shifts in facial skin caused by blood pulsing through micro-capillaries. This is a subtle signal that an RGB camera can pick up and that inert mask material cannot produce.
Research on rPPG anti-spoofing has shown genuine strength against high-quality physical masks, which is why it appears across several serious biometric platforms. It comes with an honest limitation worth noting: academic work, such as the University of Oulu’s OR-PAD study, has demonstrated that a fabricated rPPG signal can sometimes be injected into a replayed video stream. Because of this, credible technology providers treat blood-flow analysis as one signal among several rather than a standalone fix.
Identity delegation is the low-tech attack that no amount of surface texture analysis catches on its own. The monitored participant simply hands the smartphone to someone else. The defense here is not liveness detection, but the one-to-one biometric facial match, which confirms that the live human face on camera actually belongs to the enrolled subject and not to a willing substitute.
The threat landscape has evolved fastest around synthetic media, which requires a crucial distinction that many software buyers never hear. There are two distinct classes of deepfake attacks, and they demand two entirely different defensive layers:
A presentation attack shows a fake image or mask to the physical camera lens, which is what Presentation Attack Detection (PAD) is engineered to catch. An injection attack skips the camera hardware entirely, feeding synthetic video directly into the app’s data stream via a virtual camera or compromised software environment. PAD tools do nothing against data injection because there is no physical presentation to detect at the lens level. Stopping an injection attack requires Injection Attack Detection (IAD), which verifies hardware sensor integrity and data paths rather than visual realism alone.
That technical distinction is far from academic. The iProov 2026 Threat Intelligence Report, published in April 2026, recorded a 1,151 percent jump in digital injection attacks targeting iOS devices during the second half of 2025, part of a 741 percent rise across that full year. The report traced a purpose-built iOS injection tool of suspected Chinese origin that hijacks video streams on jailbroken phones.
Cybersecurity firm Group-IB logged 8,065 injection attempts against a single financial institution in just eight months of 2025. The UK government has estimated that roughly 8 million deepfakes circulated globally in 2025, up from about 500,000 in 2023, with turnkey deepfake-as-a-service software online for as little as 10 to 50 dollars. A supervision platform that advertises liveness detection without injection defense is protecting the front door while leaving the data stream exposed.
Active and Passive Liveness Detection in Real Monitoring Programs
Supervision platforms take two primary architectural approaches to liveness verification. The core operational trade-off comes down to balancing security protocols against user friction.
Passive Liveness Checks
Passive systems confirm liveness without asking the user to perform explicit on-screen actions. The application captures a rapid burst of frames in the background, analyzing natural physiological markers automatically.
- Operates invisibly during basic facial framing without requiring manual inputs.
- Reduces user confusion and speeds up check-in completion times.
- Lowers false failure rates caused by misunderstood movement prompts.
- Ideal for older participants or individuals unfamiliar with smartphone interfaces.
Passive checks serve as a sensible default for routine, low-risk community supervision, where every added second of friction translates into missed check-ins that officers must manually investigate.
Active Liveness Challenges
Active systems require the participant to perform randomized real-time prompts, such as turning their head, blinking, or tracking a moving target on screen.
- Introduces dynamic prompts that pre-recorded video clips or photos cannot predict.
- Adds a higher verification barrier for critical compliance windows.
- Requires slightly longer check-in durations and steady physical coordination.
- Serves as an effective escalation step when passive confidence scores fall near threshold limits.
The most effective supervision platforms do not force a single mode onto every participant. They run passive liveness checks as a seamless baseline, automatically escalating to active challenges when a passive score drops near warning thresholds or when a participant moves into a higher risk tier.
How Electronic Monitoring Platforms Combine GPS, Biometrics, and Liveness Detection
No single data signal can support an entire legal supervision record on its own. The defensibility of an agency’s log comes from how multiple independent security signals reinforce one another, ensuring that cheating the system requires defeating every layer simultaneously.
| Security Layer | Primary Operational Function | Specific Fraud Target Neutralized |
| GPS Location | Tracks spatial coordinates and geofence events | Flags unapproved physical movement outside designated areas |
| Time Verification | Locks check-in events to network time standards | Prevents device clock manipulation and backdated reporting |
| Facial Recognition | Compares captured face to enrolled biometric profile | Blocks unauthorized proxies or stand-ins from checking in |
| Liveness Detection (PAD) | Analyzes skin depth, texture, and natural micro-motion | Rejects printed photos, screen replays, 3D masks, and fake media |
| Injection Defense (IAD) | Validates camera hardware data paths and stream integrity | Blocks digital video injection, virtual cameras, and stream hijacking |
| Device Binding | Ties app installation to specific hardware signatures | Stops phone swapping and Android or iOS software emulators |
| Audit Logging | Generates tamper-evident, cryptographically signed files | Produces court-admissible evidence for judicial hearings |
The true strength of this multi-factor architecture lies in simultaneity. A valid check-in requires the registered hardware, the correct geographic coordinates, a matching facial template, verified live presence, and a clean data stream at the same moment.
Where Liveness Detection Delivers the Most Value
Biometric presence verification proves its worth across varied judicial, correctional, and rehabilitative settings, with its operational value adjusting to the specific demands of each program.
Home Confinement and Curfew Management
House arrest programs require strict compliance checks at irregular hours throughout the day and night. Automated liveness checks confirm that a confined individual is actually inside the residence, rather than proving a smartphone was left at home while its owner went elsewhere.
Platforms like Shadowtrack, built for home-detention caseloads, prompt an average of four to five randomized check-ins daily. These platforms leverage facial recognition as the primary verification layer and fall back to voice verification if visual capture fails, preventing isolated environmental glitches from generating false violation records.
Community Supervision and Probation
Probationers holding steady jobs cannot afford to miss work shifts for routine office visits. Remote check-in windows backed by robust liveness detection allow caseworkers to maintain meaningful oversight without disrupting employment schedules.
Applications in this space, including Attenti’s aCheck and BI’s SmartLINK, pair biometric check-ins with automated self-reporting modules, ensuring low-risk cases consume significantly less officer time while keeping oversight intact.
Alcohol and Rehabilitation Monitoring
Remote sobriety testing is an area where proxy fraud is an obvious threat, making biometric presence the most direct solution. Dedicated hardware like Soberlink pairs a court-admissible breathalyzer with integrated facial recognition and tamper sensors. Every breath test is linked to the correct individual at the precise moment the sample is blown, giving family courts and treatment providers full confidence in unwitnessed results. Modules like Shadowtrack’s ShadowBriety and Sentinel’s remote alcohol testing follow the same design logic by locking breath testing directly to a verified face.
Court-Ordered Pretrial Reporting
Individuals on conditional release before trial must demonstrate ongoing compliance without burdening court facilities. Automated liveness check-ins reduce administrative strain on pretrial staff while maintaining a detailed, timestamped record for judges and attorneys.
This verification depth directly impacts program outcomes. A randomized controlled study on pretrial GPS monitoring in Cook County, published in 2024, demonstrated that structured electronic monitoring lowered failure-to-appear rates without increasing pretrial misconduct. Reliable identity verification is what allows public agencies to stand behind those numbers in court.
Building Trust Without Creating Unnecessary Friction
Deploying biometric verification within community corrections is as much a user-experience challenge as it is a technical security requirement. If an application workflow is overly complex, dropped connections or failed scans get flagged as non-compliance, eroding participant trust and swamping officers with manual violation appeals.
Fast processing speed serves as the first line of defense against system friction. Verification checks that wrap up in seconds hold up under poor cellular coverage and run reliably on budget mobile devices. Environmental variables must also be handled by software design rather than user penalties:
- Low ambient lighting and lower-resolution camera sensors require algorithmic exposure adjustments instead of automatic rejections.
- Algorithmic fairness is a fundamental requirement. Ongoing benchmark testing by NIST has highlighted demographic variance in facial recognition error rates across different software engines.
- A liveness platform trained on narrow datasets can fail more frequently when processing specific skin tones, age groups, or facial structures.
- Supervision agencies should require audited demographic performance data from software vendors rather than accepting general accuracy claims.
Finally, resilient offline software modes should encrypt and queue check-in data locally whenever network connectivity drops. The application then uploads the verified event log automatically once cellular service returns, ensuring a temporary dead zone is never logged as a missed report.
Protecting Biometric Data Throughout the Monitoring Process
Facial data represents sensitive personal information, and handling it carelessly exposes agencies to regulatory penalties alongside privacy risks. Multiple states regulate biometric data collection directly, with Illinois’s Biometric Information Privacy Act (BIPA) standing out as a strict benchmark. BIPA grants individuals a private right to sue over mishandled biometric records, resulting in major legal settlements. Texas and Washington enforce their own biometric statutes, meaning any supervision program operating across regions must design its technical stack to meet the highest legal standard.
Cryptographic baseline security begins with encrypting biometric data both while traveling across mobile networks and while stored inside cloud databases. Advanced platforms avoid storing raw video files or source photographs permanently. Instead, they transform each capture into a mathematical biometric template, creating a vector representation from which a human face cannot be reverse-engineered or reconstructed.
Clear data retention protocols must define when biometric vector logs are permanently deleted after a participant completes their program. Strict access controls should restrict database permissions strictly to authorized case managers, establishing firm software barriers against sharing biometric records with outside law enforcement or commercial databases.
What to Evaluate Before Deploying a Liveness Detection Platform
Agency leadership evaluating liveness verification providers should treat third-party testing as an essential baseline rather than taking vendor claims at face value. Assessing several technical criteria helps separate a field-proven platform from a basic demonstration app:
- Presentation Attack Detection (PAD) Certification: Confirm adherence to international standards like ISO/IEC 30107-3, validated by an accredited laboratory such as iBeta. Clarify the target testing level. Level 1 evaluates basic 2D prints and screen replays, Level 2 tests 3D silicone masks, and Level 3 introduces hyper-realistic custom masks under red-team testing.
- Injection Attack Detection (IAD) Capabilities: Verify that IAD is treated as a distinct defense layer. Look for testing aligned with CEN/TS 18099 specifications or formal FIDO Face Verification certifications to ensure deepfake injection vectors are blocked.
- NIST SP 800-63-4 Framework Alignment: The April 2025 revision of NIST Digital Identity Guidelines made PAD mandatory for higher-assurance applications while introducing explicit guidance for digital injection and synthetic media controls.
- Independent Error Rate Benchmarks: Request verified Attack Presentation Classification Error Rates (APCER) along with Bona Fide Presentation Classification Error Rates (BPCER) from external lab reports. A system configured to reject every check-in might seem secure, but it breaks down operationally.
- Demographic Performance Verification: Inspect software performance metrics broken down by skin tone, age, and gender to ensure the engine does not produce disproportionate rejection rates for specific groups.
- Lightweight Mobile SDK Integration: Confirm the client software runs efficiently on entry-level mobile hardware without causing excessive battery drain or thermal throttling.
- API Integration: Ensure the liveness engine syncs directly with existing agency case management platforms via documented APIs, allowing verified check-ins to land in official participant records without manual data entry.
Selecting verification tech built on independently audited standards gives community supervision programs long-term security and clear defensibility when identity records are questioned in legal proceedings.
Final Thoughts
Modern electronic monitoring relies on confirming two variables continuously: where a person is located and who that person actually is. Standard GPS tracking answers the spatial question well, but it cannot address identity because location coordinates track hardware, and hardware carries no personal identity.
Liveness detection provides the missing operational layer by confirming live human presence during every check-in event. This capability neutralizes physical photos, screen video replays, silicone masks, and presentation deepfakes. The monitoring programs that remain effective over the coming years will be those that treat liveness detection as a vital component within a broader security strategy.
By pairing liveness detection with dedicated injection attack defense, binding verification data to hardware signatures and GPS coordinates, and relying on audited platform testing, agencies can build a reliable system. Structured this way, remote monitoring produces a clear oversight log that officers can trust, and courts can rely on.